[Bah-general] CLICKJACKING

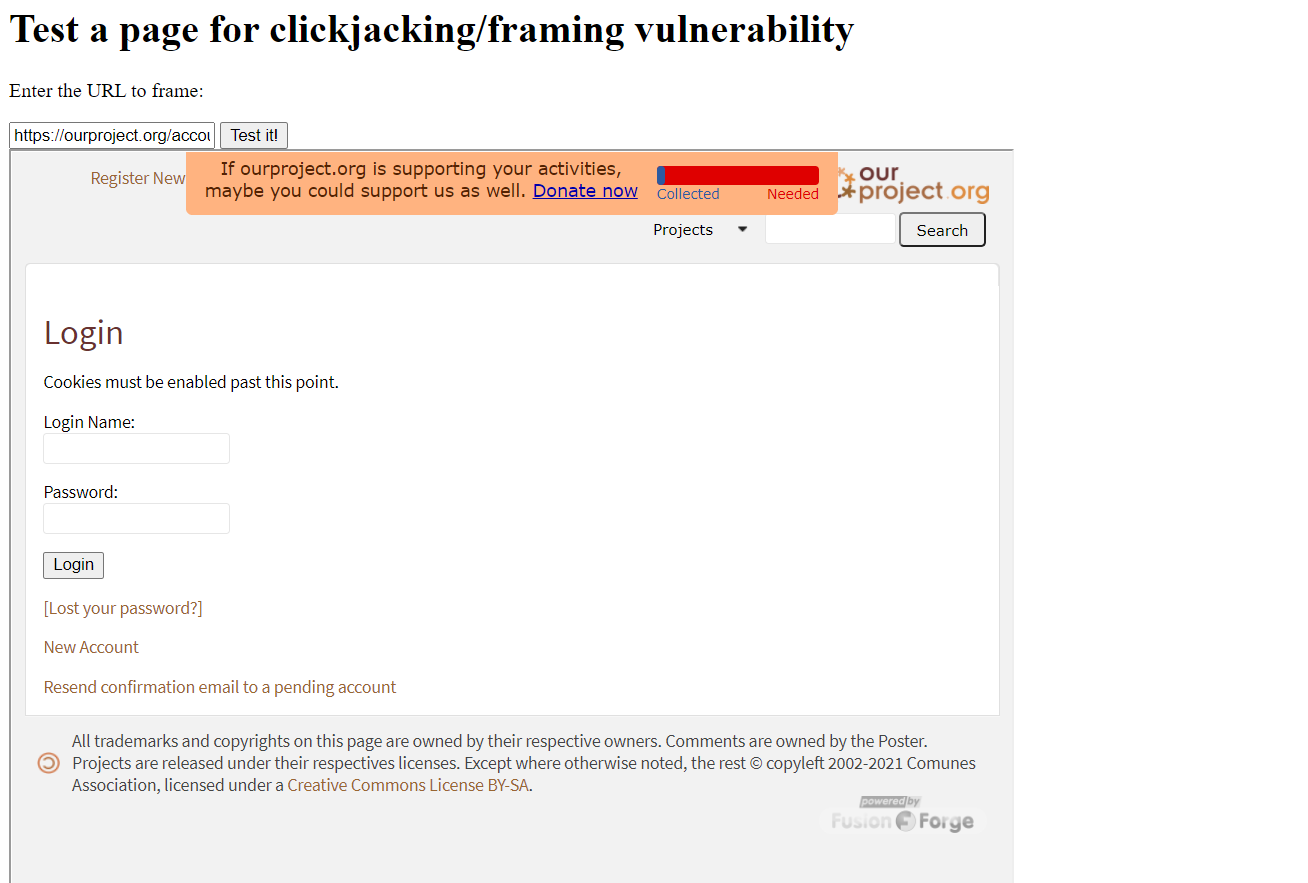
[image: Capture.PNG] Hello team, Hope you are fine. I am a security researcher and have found some bugs/vulnerabilities in your website. BUG TYPE: CLICKJACKING In the index (home page): https://website.com/login Clickjacking, also known as a "UI redress attack", is when an attacker uses multiple transparent or opaque layers to trick a user into clicking on a button or link on another page when they were intending to click on the top-level page. Thus, the attacker is "hijacking" clicks meant for their page and routing them to another page, most likely owned by another application, domain, or both. Using a similar technique, keystrokes can also be hijacked. With a carefully crafted combination of style sheets, iframes, and text boxes, a user can be led to believe they are typing in the password to their email or bank account, but are instead typing into an invisible frame controlled by the attacker. PoC: <html> <head> <title>test nbxsites </title> </head> <body> <p> https://website.com/login is vulnerable to clickjacking!</p> <iframe src="https://website.com/login" width="500" height="500"></iframe> </body> </html> IMPACTS: Tricking a user into unknowingly; No.1: An attacker can gain access to the credentials of users and use those credentials for booking and payment. No.2: adding events to their profile they are interested in attending. No. 3: editing their star rating on reviews; No.1: bookmarking unwanted business PROOF: ss Best Regards. Found More bugs on your website reply to me so that I may disclose them further <https://www.avast.com/sig-email?utm_medium=email&utm_source=link&utm_campaign=sig-email&utm_content=webmail> Virus-free. www.avast.com <https://www.avast.com/sig-email?utm_medium=email&utm_source=link&utm_campaign=sig-email&utm_content=webmail> <#DAB4FAD8-2DD7-40BB-A1B8-4E2AA1F9FDF2> _______________________________________________ Bah-general mailing list [email protected] https://lists.ourproject.org/cgi-bin/mailman/listinfo/bah-general
participants (1)
-
 secure head